How to Create an SPF Record for Your Domain
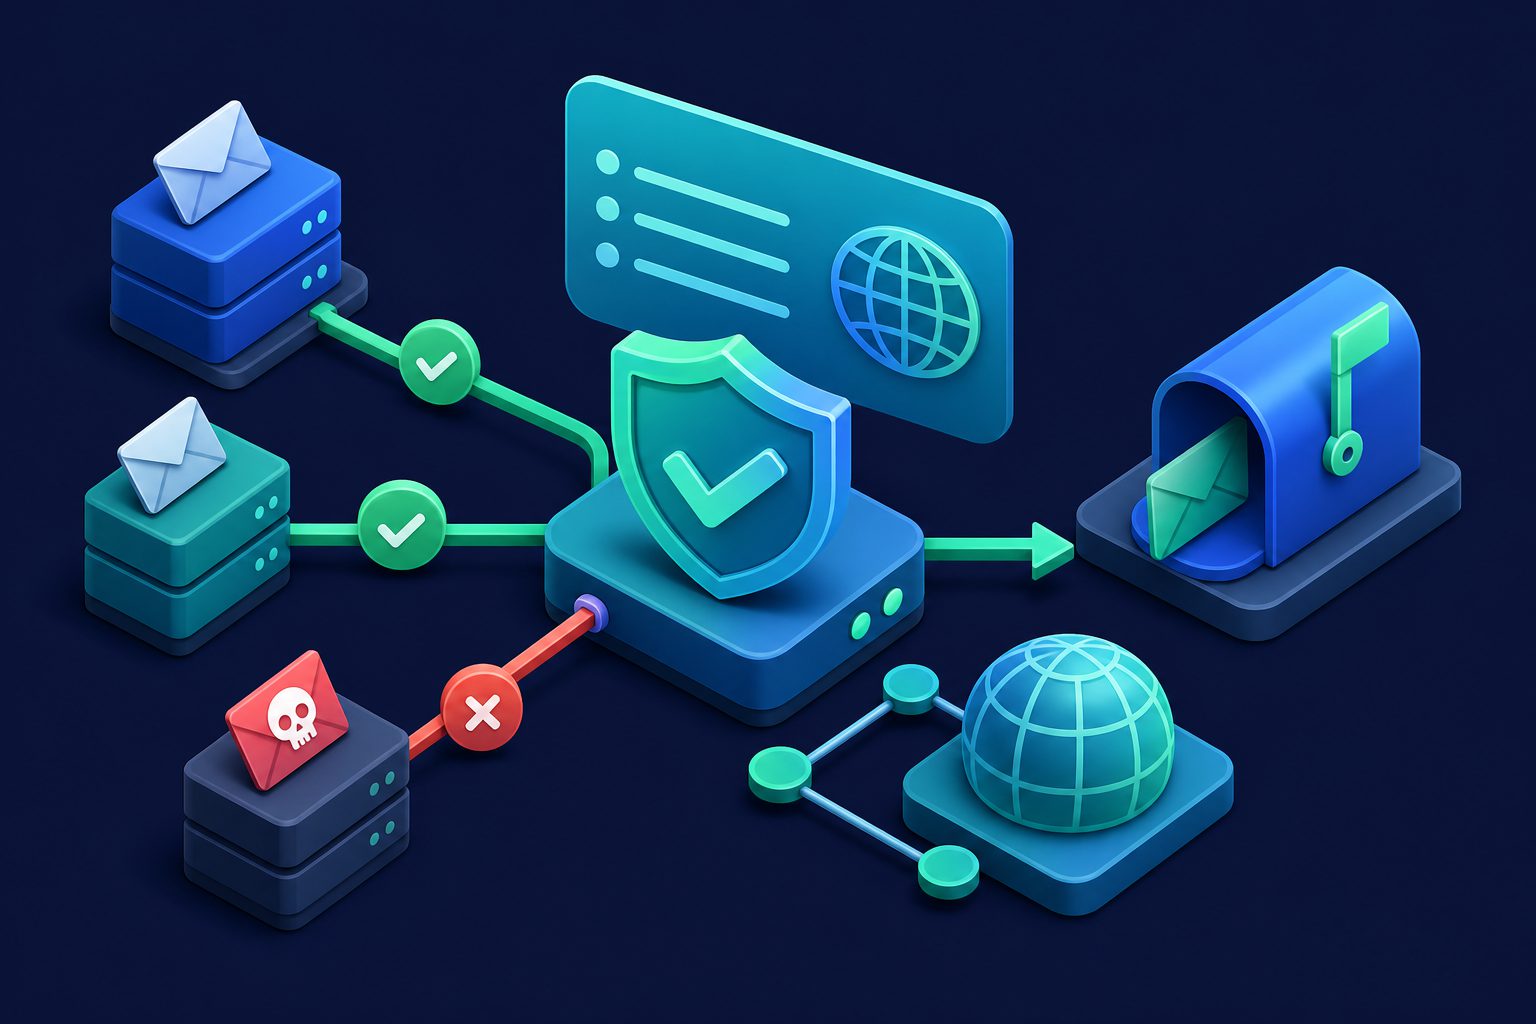
An SPF record is a single line of text in your domain's DNS that lists every server authorized to send email on your behalf. When a receiving mail server gets a message claiming to be from your domain, it checks your SPF record. If the sending server is not listed, the message fails authentication and is more likely to be rejected or flagged as spam.
Without an SPF record, anyone can send email that appears to come from your domain. With a misconfigured one, your own legitimate email may fail delivery. Getting SPF right is one of the most impactful things you can do for your domain's email security and deliverability.
What an SPF record looks like
An SPF record is a DNS TXT record on your root domain. Here is a typical example:
v=spf1 include:_spf.google.com include:mail.cleanbox.app mx -allBreaking this down:
| Part | Meaning |
|---|---|
v=spf1 | Identifies this as an SPF record (required, always first) |
include:_spf.google.com | Authorize Google Workspace's mail servers |
include:mail.cleanbox.app | Authorize Cleanbox's mail servers |
mx | Authorize whatever servers your MX records point to |
-all | Reject everything not explicitly listed (strict policy) |
Build your SPF record step by step
You can use our free SPF generator tool to build your record visually, or follow these steps manually:
Step 1: Identify all your sending sources
List every service and server that sends email using your domain name. Common sources include:
- Your email provider — Google Workspace, Microsoft 365, Fastmail, Zoho, or your own mail server
- Your website — Contact forms, order confirmations, password resets
- Marketing tools — Mailchimp, Sendinblue, ConvertKit, HubSpot
- Transactional email — SendGrid, Postmark, Amazon SES, Mailgun
- CRM and support — Zendesk, Intercom, Freshdesk
- Cleanbox Relay — If you use Cleanbox Relay for inbound filtering
Missing a source means that service's emails will fail SPF checks. Adding a source you do not use weakens your record unnecessarily.
Step 2: Find each source's SPF include
Every email service publishes the value you need to add. Here are the most common ones:
| Service | SPF include |
|---|---|
| Google Workspace | include:_spf.google.com |
| Microsoft 365 | include:spf.protection.outlook.com |
| Zoho Mail | include:zoho.com |
| Fastmail | include:spf.messagingengine.com |
| Mailchimp | include:servers.mcsv.net |
| SendGrid | include:sendgrid.net |
| Amazon SES | include:amazonses.com |
| Postmark | include:spf.mtasv.net |
| Mailgun | include:mailgun.org |
| Cleanbox | include:mail.cleanbox.app |
If your service is not listed, check their documentation for “SPF setup” or “email authentication.”
Step 3: Decide on the a and mx mechanisms
a— Authorizes the IP address your domain's A record points to. Use this if your web server also sends email (contact forms via sendmail, for example)mx— Authorizes the IP addresses of your MX record servers. Use this if your mail server both receives and sends email from the same IP
If all your sending goes through a hosted service (Google, Microsoft), you typically do not need a or mx. The include directives cover everything.
Step 4: Add specific IP addresses (if needed)
If you run your own mail server or have a service that sends from a fixed IP, add it directly:
ip4:203.0.113.10— Authorize a single IPv4 addressip4:203.0.113.0/24— Authorize an IPv4 rangeip6:2001:db8::1— Authorize an IPv6 address
Step 5: Choose your policy
The policy at the end of your SPF record tells receiving servers what to do with messages that do not match any authorized source:
| Policy | Meaning | When to use |
|---|---|---|
-all | Hard fail — reject unauthorized senders | When you are confident your record lists all sources (recommended) |
~all | Soft fail — accept but mark as suspicious | During initial setup when you are still testing |
?all | Neutral — no opinion on unauthorized senders | Rarely useful; offers no protection |
Start with ~all while testing, then switch to -all once you have confirmed all legitimate email passes. Use our SPF checker tool to verify your record after publishing.
Step 6: Assemble and publish
Combine everything into a single TXT record:
v=spf1 include:_spf.google.com include:sendgrid.net ip4:203.0.113.10 -allAdd this as a TXT record on your root domain (not a subdomain) in your DNS provider. For step-by-step DNS setup instructions for specific providers, see our DNS setup guide for Cloudflare, GoDaddy, and Namecheap.
Common SPF mistakes
Too many DNS lookups
SPF has a hard limit of 10 DNS lookups per evaluation. Each include, a, mx, and redirect mechanism counts as one lookup. Nested includes (an include that includes another include) count toward your total. If your record exceeds 10 lookups, it fails entirely — not just the extra parts, all of it.
Use our SPF checker to count your current lookups. If you are close to the limit, consider replacing include directives with direct ip4 entries where possible, or using an SPF flattening service.
Multiple SPF records
A domain must have exactly one SPF record. Two TXT records that both start with v=spf1 cause a permanent error — receivers treat the result as if no SPF record exists. If you need to add a source, edit your existing record. Do not add a second one.
Forgetting a sending source
The most common SPF failure: a service sends email from your domain but is not listed in your SPF record. The symptoms are subtle — most of those emails still deliver (especially to Gmail), but they fail SPF checks, which affects your DMARC alignment and can eventually hurt deliverability.
Using +all
An SPF record ending in +all explicitly authorizes every server on the internet to send email from your domain. This is worse than having no SPF record at all, because it signals intentional openness rather than a missing configuration.
Verify your SPF record
After publishing your record, verify it immediately:
- Use the Cleanbox SPF Checker to validate the syntax, count DNS lookups, and confirm the policy
- Send a test email from every authorized source and check the headers for
spf=pass - Check your DMARC record to make sure SPF results feed into your DMARC policy
SPF alone is not enough
SPF verifies which servers can send for your domain, but it does not verify the visible “From” address in the email client. An attacker can pass SPF by sending from their own authorized server while spoofing your domain in the display address.
Complete email authentication requires three records working together:
- SPF — Authorizes sending servers (use the SPF generator)
- DKIM — Cryptographically signs messages to prove they were not altered (verify with the DKIM checker)
- DMARC — Ties SPF and DKIM together and tells receivers what to do when both fail (check with the DMARC lookup)
For the full picture, see our complete guide to SPF, DKIM, and DMARC.
Use the free SPF generator
If you prefer not to assemble the record manually, our free SPF record generator lets you select your sending sources, add IP addresses, choose your policy, and copy the finished record. It handles the syntax so you can focus on what to include.
Need to protect the email that arrives at your domain too? Create a free Cleanbox account to filter spam, phishing, and malware before they reach your inbox.
Ready to take control of your inbox?
Start protecting your email with Cleanbox — free plan available, no credit card required.
Get started free